XRP Ledger’s Payment Engine Had a Counterfeiting Bug Hiding Since 2015
In brief
- XRP Ledger maintainers disclosed and patched a critical payment-engine overflow bug, reported via bug bounty in September, that could have let an attacker create counterfeit XRP.
- The flaw sat unnoticed since 2015 because no normal payment triggers it, and the ledger’s “no XRP created” safety check used the same broken arithmetic.
- There is no evidence the bug was ever exploited, XRP Ledger devs say.
Developers behind the XRP Ledger have disclosed and fixed a critical vulnerability that, left unaddressed, could have let an attacker conjure XRP out of thin air, a flaw that sat dormant in the network’s code for roughly a decade.
In a disclosure published Friday, the ledger’s maintainers said a researcher reported the bug through the XRPL bug bounty program in September. The issue was an integer overflow in the payment engine, the part of the software that processes payments.
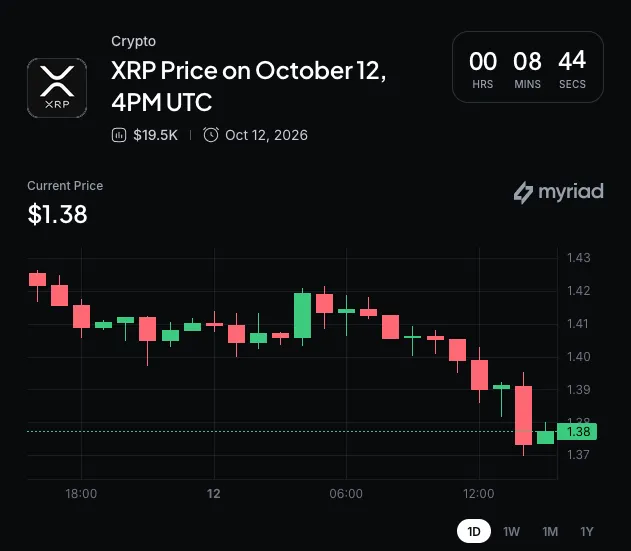 Myriad: Where does XRP go next? Click to make your prediction.
When a single payment consumed hundreds of specially crafted offers from the order book, the sum of what the buyer owed exceeded the maximum value the system could store and “wrapped around” to a tiny number. The engine paid each seller in full but charged the buyer almost nothing, with the difference amounting to newly minted XRP that should never have existed.
Worse, the ledger’s built-in safety check meant to confirm no transaction creates XRP used the same flawed arithmetic, so it wrapped around identically and caught nothing. The maintainers said an attacker could have created spendable XRP far beyond the token’s total supply in a single transaction, then moved it, traded it or sent it to exchanges.
RippleX engineers confirmed the bug had been present since the current payment engine was written in 2015 and went unnoticed because no ordinary payment comes anywhere near triggering the overflow.
There is no evidence it was ever exploited, the team said. The fix shipped in version 3.4.1 on Sept. 25, and more than 80% of the network’s trusted validators were running it that day.
Notably, the patch bypassed the ledger’s usual amendment process, which requires validators to vote and wait two weeks before a change takes effect, the first time a transaction-processing change has deliberately shipped that way since the system was introduced over a decade ago. The maintainers said the severity justified it, since the open-source fix would have revealed the bug while leaving it exploitable for weeks.
The disclosure echoes a counterfeiting scare that rocked Zcash this year, when the privacy coin raced to patch a soundness bug in its shielded pool that could have allowed forged coins. That episode sent ZEC tumbling before the network’s Ironwood upgrade resolved it.
XRP didn’t escape the week unscathed. The token traded at $1.38 on Monday, down 1.6% over 24 hours, the worst performance among major cryptocurrencies, and off 9.4% over the past seven days.
Daily Debrief Newsletter
Start every day with the top news stories right now, plus original features, a podcast, videos and more.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Comments (0)