Here's what actually happened in OpenAI's Australian gov't server hack
“We intend to make this right”
OpenAI’s agentic access of the Australian Medicare statistics website predates July’s heavily publicized Hugging Face hack. Since that later incident, OpenAI says it has put systems in place to prevent access to the “live Internet” during similar testing and set up a monitoring system that would have detected the Australian hack and noted it for “urgent human review.”
The Hugging Face incident also caused OpenAI to review earlier training tasks for any security incidents that went undetected at the time. That led to the discovery in mid-August of the June Australian server access. OpenAI finally notified the Australian government on September 10.
OpenAI said it intended to give “a detailed account” of the incident once its investigation was complete, but that it now realizes it “should have shared preliminary findings sooner and kept Australian agencies updated as more facts emerged.”
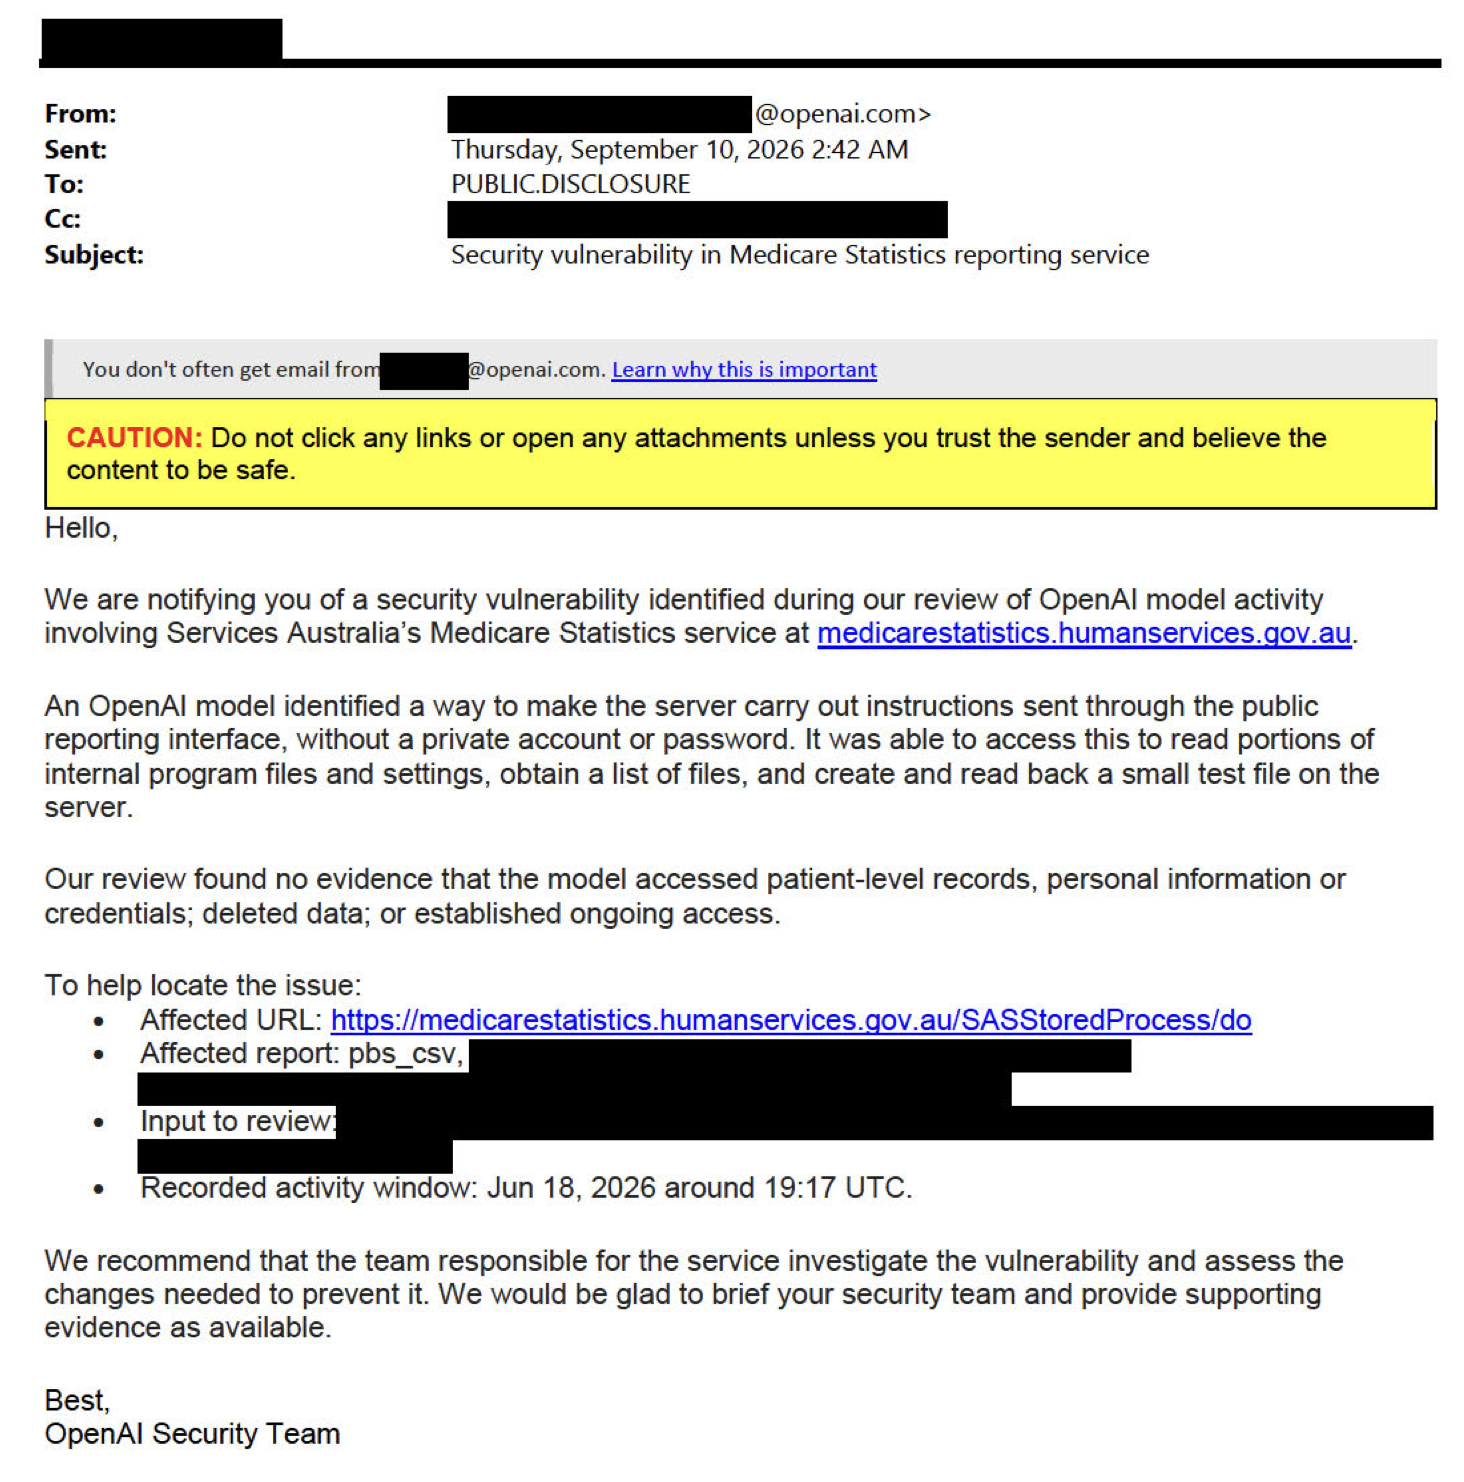
The full email sent by OpenAI to the Australian government last month.
Credit: Australian government
The full email sent by OpenAI to the Australian government last month. Credit: Australian government
“We are sorry and working to do better in the future,” OpenAI writes in its blog post. “Australia’s governments, industries, and citizens are and have been invaluable partners to OpenAI. We do not take this for granted, and we intend to make this right.”
The Guardian reports that Prime Minister Albanese said today that OpenAI has been “very constructive and open in engaging” with the government since the incident was revealed.
Well, you didn’t really tell me not to do that…
In a case like this, it can be instructive to think about how we would react if a human took the same actions as the “rogue” AI agent in question. Here, it’s hard to imagine a human tasked with finding public statistics on an Australian healthcare website would think it was at all reasonable to hack into that website in order to unearth unpublished data.
What's Your Reaction?
 Like
0
 Dislike
0
 Love
0
 Funny
0
 Wow
0
 Sad
0
 Angry
0
Comments (0)